Version 1.0 — Now Available

Security analysis for
5G-critical code

Detect buffer overflows, format string attacks, command injections, and 20+ vulnerability classes in C/C++ codebases. Powered by three analysis engines and local LLM reasoning.
Windows 10+ · 101 MB · Free & Open Source

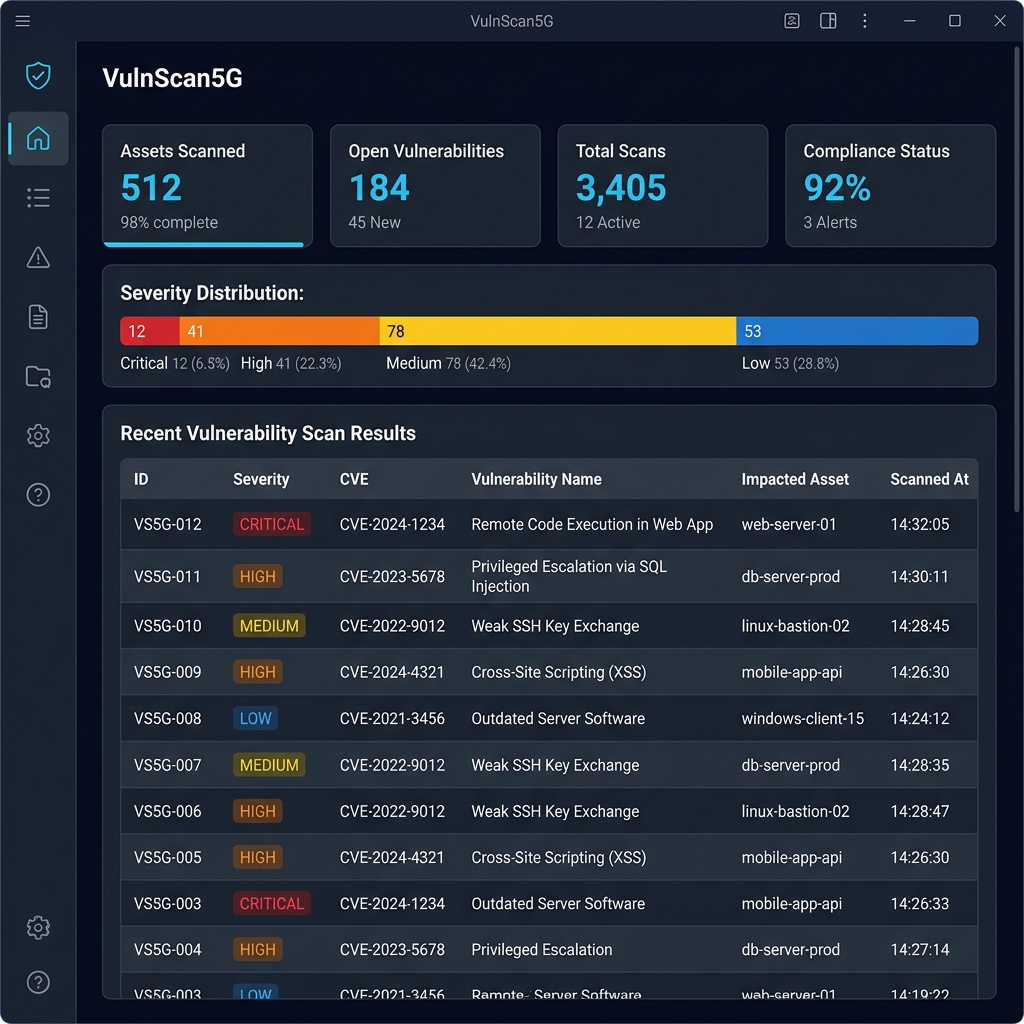
VulnScan5G desktop application showing vulnerability scan results
25
Detection Rules
3
Analysis Engines
10+
CWE Categories
100%
Local Processing

Built for security teams

Everything you need to find, understand, and fix vulnerabilities in C/C++ code — from quick scans to AI-assisted remediation.

Triple-Engine Detection

Regex pattern matching, pycparser AST analysis, and tree-sitter parsing work together to minimize false negatives across C and C++ code.

LLM-Powered Reasoning

Optional local AI reasoning via Ollama confirms or rejects findings, explains vulnerabilities in context, and generates targeted code fixes.

Auto-Fix Generation

One-click fix generation produces patched source files. Review diffs side-by-side and apply fixes selectively or in bulk.

5G-Focused Rules

Purpose-built for the vulnerability classes that matter most in 5G infrastructure — buffer overflows, race conditions, command injection, and more.

Rich Reporting

Export findings as interactive HTML dashboards or structured JSON. Filter by severity, search across rules, and share results with your team.

Fully Offline

All analysis runs locally on your machine. Source code never leaves your environment — no cloud uploads, no external APIs required.

25 rules across 10+ CWE categories

Comprehensive coverage of the most critical vulnerability classes found in C and C++ codebases.

CWE-120

Buffer Overflow

gets(), strcpy(), sprintf(), scanf %s, memcpy with variable sizes

CWE-78

Command Injection

system(), popen() with user-controlled input

CWE-134

Format String

printf(var), fprintf(f, var) with non-literal format strings

CWE-416

Use-After-Free

free() without NULL assignment, double free detection

CWE-190

Integer Overflow

malloc(a * b), realloc(p, n + m) without overflow checks

CWE-367

Race Conditions

access() then open(), TOCTOU pattern detection

CWE-476

NULL Dereference

Unchecked malloc(), realloc() return values

CWE-401

Memory Leaks

malloc in loops without corresponding free

Seven-stage analysis pipeline

From file discovery to remediation — each stage is designed for accuracy and speed.

1

Ingest

Discover .c, .cpp, .h, .hpp files recursively

2

Preprocess

Strip comments, normalize whitespace

3

Detect

Regex + AST + tree-sitter scanning

4

Merge

Deduplicate, assign CWEs, score

5

Reason

LLM confirms or rejects findings

6

Fix

Generate patches automatically

7

Report

Console, JSON, or HTML output

Get VulnScan5G

Free and open source. Install on Windows and start scanning in under a minute.

Download VulnScan5G v1.0.0
Windows 10+
v1.0.0 · 101 MB
MIT License